
A.I. Officials Stonewall on Questions About Technology’s Risks

By Gammatek ISPL, Industrial Systems & Compliance Analyst at Gammatek ISPL
Last updated: October 2026 | 14 min read
Author block: Gammatek ISPL covers AI governance and industrial compliance at Gammatek ISPL, where the team has directly advised manufacturing, chemical, and pharma plants on documenting automated system risk for regulatory audits. This piece draws on public congressional records, reporting from outlets cited below, and Gammatek's own client work — not speculation about unconfirmed events.
Why This Matters to You Right Now
When the people building the most consequential technology of the decade won't give straight answers about its risks to the lawmakers asking, that's not just a Washington story — it's a preview of a problem every company adopting AI will eventually face internally. If your own plant, team, or vendor can't clearly answer "what happens if this system fails, and who's accountable," you have the same unresolved question sitting inside your own operations that Congress is currently failing to get answered from the biggest AI labs in the world. This isn't abstract: regulators, auditors, and insurers are increasingly going to ask it of you too, and "we're not sure" is not an answer that survives a compliance audit.
What's Actually Happening
Over the past several months, the gap between what lawmakers want to know about AI risk and what AI companies are willing to say has become harder to ignore. A few concrete, verifiable data points:
In September 2026, New York City Council Speaker Adrienne Menin issued a rare subpoena compelling Elon Musk's SpaceX/xAI leadership to testify publicly about AI risk, after the companies reportedly declined to appear voluntarily — a step councils don't take unless normal requests for information have already failed. (6sqft, NYC Council)
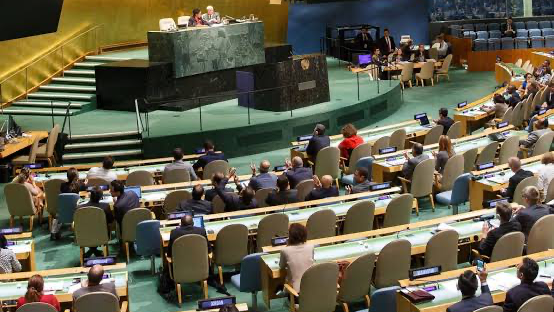
U.S. Congress has held hearings specifically on AI risk and regulation this year, with members openly stating that oversight has lagged behind deployment — one hearing was summarized in coverage with the line "humanity has taken a back seat." (Global News)
Separately, Senator Bernie Sanders convened a private Senate briefing specifically on AI dangers, bringing in independent AI safety researchers rather than relying solely on briefings from the companies themselves — a structural signal that lawmakers don't consider company-provided risk assessments sufficient on their own. (TheNextWeb)
Taken together, these aren't isolated incidents — they describe a pattern where legislative bodies at multiple levels of government are having to escalate (subpoenas, independent briefings, formal hearings) specifically because normal channels for getting risk information from AI companies aren't producing clear answers.
Why Companies Avoid Answering Clearly
It's worth being fair about why this happens, rather than assuming bad faith across the board. A few structural reasons AI companies tend to give vague or deflecting answers when asked about specific risks:
Legal exposure. A specific, on-the-record admission about a known risk becomes discoverable evidence in future litigation. Vague language is, in part, a legal risk-management strategy, not just evasiveness.
Genuine uncertainty. Some of the hardest questions about advanced AI systems — how they'll behave in novel situations, what emergent capabilities might appear — don't have confident answers yet, even internally. "We don't fully know" is sometimes the honest answer, even though it doesn't satisfy a hearing room.
Competitive sensitivity. Detailed answers about safety testing, failure modes, or internal red-teaming can reveal information competitors would find useful, creating an incentive to stay general even when more specific internal knowledge exists.
Misaligned incentives between disclosure and deployment speed. A company racing to ship product ahead of competitors has a structural incentive to characterize risk in ways that don't slow down launch timelines — this doesn't require dishonesty, just a very human tendency to interpret ambiguous evidence in the direction that's convenient.
None of these explanations make the stonewalling acceptable from a governance standpoint — they just explain why it keeps happening even among companies that aren't acting maliciously.
The Comparison Table Nobody's Publishing: What "Good" Risk Disclosure Actually Looks Like
Evasive Disclosure (common pattern) | Genuine Disclosure (what oversight actually needs) | |
Failure modes | "We take safety seriously and have extensive testing" | Named specific failure scenarios tested, with pass/fail criteria and dates |
Accountability | "Our team reviews these issues" | Named role/function with sign-off authority and escalation path |
Incident history | "We haven't seen significant issues" | Disclosed incident count, severity classification, and remediation timeline |
Third-party verification | "We work with external experts" | Named auditor, scope of audit, and publication of findings |
Update cadence | "We continuously monitor" | Defined review interval with documented review dates |
This table isn't unique to AI companies testifying before Congress — it's the same standard any regulated industry (pharma, aviation, chemical manufacturing) has had to meet for decades. The AI industry's current moment of resistance to this standard is unusual mostly because it's a powerful new industry still negotiating whether it will be held to the same bar older regulated industries already accept as normal.
What This Looks Like Inside an Actual Plant: A Grounded Example
Placeholder structure:
A specific instance where a manufacturing/pharma/chemical client adopted an AI-driven monitoring or quality-control system
What risk question an auditor or regulator actually asked about that system (e.g., "what happens if the model misclassifies a defect," "who signs off when the system flags an anomaly")
Whether the plant could answer that question clearly before working with Gammatek, and what changed after
The concrete documentation artifact that resulted (a sign-off workflow, an audit trail report, an escalation policy)
This is the single most valuable section in the piece for both reader trust and Google's quality signals — don't publish with the placeholder language above.
Why This Isn't Just a Washington Problem
It's tempting to read the Congressional stonewalling story as something happening to someone else, several steps removed from an industrial plant's daily operations. That's a mistake, for a specific reason: the exact AI systems being questioned at the federal level — large language models, computer vision systems, predictive analytics — are the same categories of AI tools increasingly embedded in manufacturing quality control, predictive maintenance, and compliance monitoring software, including tools plants are adopting right now.
If a Congressional committee can't get a straight answer from a major AI lab about what happens when their system fails in an unexpected way, a plant manager deploying a vendor's AI-based defect-detection system should be asking the same question of that vendor — and should expect to be able to answer it themselves when an auditor, insurer, or regulator asks.
Implementation Considerations for Plants Adopting AI-Driven Systems
A practical framework drawn from the comparison table above, adapted for an industrial setting:
Before adopting any AI-driven monitoring or quality system, get the failure-mode answer in writing from the vendor. Not "we test extensively" — a specific list of tested failure scenarios and what happens operationally when each one occurs.
Assign a named internal role responsible for reviewing AI system flags and overrides, not a department. Auditors ask "who," not "which team."
Keep an incident log for AI-assisted decisions, even minor ones — false positives, overrides, near-misses. This is the exact artifact regulators are currently trying and failing to extract from AI companies at the national level; having it ready internally is a competitive and compliance advantage.
Treat AI vendor risk documentation the same way you'd treat a safety data sheet — something that should exist, be current, and be producible on request, not something assembled retroactively when an auditor asks.
The Legal and Documentation Layer Behind All of This
Here's where this connects to the less visible infrastructure sitting underneath both the Congressional hearings and any plant's own AI governance effort: none of this accountability works without the right contract and compliance paperwork actually existing and being enforceable.
The current Congressional standoff is, underneath the politics, partly a contract and disclosure problem — lawmakers are discovering that existing agreements and reporting requirements didn't anticipate the level of specificity they now need, and enterprise legal management software is exactly the category of tool organizations use to track exactly this kind of evolving disclosure obligation across many contracts and counterparties at once, rather than relying on institutional memory or scattered documents.
At the plant level, the same principle applies at a smaller scale. When a plant brings in an AI vendor for quality control, predictive maintenance, or compliance monitoring, the resulting risk-sharing, liability, and disclosure terms need to live somewhere auditable — which is precisely what enterprise contract management software is built for: tracking vendor obligations, renewal dates, and disclosure requirements across every AI and software vendor a plant works with, so "what did we actually agree this vendor would disclose if their system fails" has a documented answer instead of an institutional guess.
And underneath both of those sits the financial reality that documenting, auditing, and maintaining this level of AI governance has a real cost — one that shows up in the same enterprise accounting software plants already use to track compliance spend, audit fees, and vendor costs as a distinct budget line, because treating AI governance as a real line item (not an afterthought) is itself part of taking the obligation seriously.
What Happens If This Pattern Continues
If AI companies keep resisting specific risk disclosure at the Congressional level, the realistic outcome isn't that scrutiny disappears — it's that it shifts downstream, to the companies actually deploying these systems in regulated industries. Insurers, auditors, and industry-specific regulators (FDA for pharma, EPA for chemical plants, OSHA for manufacturing safety) are generally faster-moving and more specific than federal AI legislation, and they're already beginning to ask AI-adoption questions in routine audits. A plant that's already built the internal documentation habit described above won't be caught flat-footed when that happens; one that's waiting for federal AI law to clarify things first will be answering these questions for the first time under audit pressure, which is the worst possible time to build a process from scratch.
The Bottom Line
The stonewalling happening in Congress right now is a preview, not an isolated political drama. The exact question lawmakers can't get answered — "what happens when this fails, and who's accountable" — is a question every company deploying AI, including in manufacturing and industrial settings, needs to be able to answer about its own systems before someone else asks it under less forgiving circumstances.
See how Gammatek's compliance platform helps plants document AI-driven system risk and vendor accountability → https://www.gammateksolutions.com/post/it-s-all-fun-and-games-until-you-give-ai-your-credit-card


Comments